Meta Extends Confidential Computing to AI Glasses with Private Processing
Quick Answer
Meta has introduced Private Processing for AI glasses, utilizing confidential virtual machines (CVMs) to handle sensitive workloads while maintaining user privacy.
Quick Take
This architecture supports advanced features like streaming transcription and contextual search, while ensuring that personal data remains secure and inaccessible to Meta.
Key Points
- Private Processing architecture uses Trusted Execution Environments (TEEs) for secure data handling.
- AI glasses can perform basic tasks locally, while advanced features require cloud processing.
- Meta is collaborating with security firms to review the architecture and attestation mechanisms.
- Persistent state and user context are encrypted and remain within the confidential boundary.
- Deployment of Private Processing on Meta's glasses is not yet available, with no timeline provided.
📖 Reader Mode
~3 min readMeta has extended Private Processing to AI glasses, using confidential virtual machines (CVMs) for sensitive AI workloads and persistent user context in the cloud. The design combines Trusted Execution Environment (TEEs), remote attestation, anonymous credentials, OHTTP, and encrypted storage. Meta says it supports streaming transcription, contextual search, and long-term recall requiring more computing and persistent state.
Basic interactions, such as calls and messages, can run on the glasses, while more advanced workloads require larger models and access to personal context accumulated over time. Meta introduced Private Processing for WhatsApp and Meta AI in 2025 and is now extending the architecture to wearable AI workloads.
Oskar Linde, VP of XR Technologies at Meta, described the approach on LinkedIn as a way to make AI more useful throughout the day while supporting the stateful, personal context required by AI glasses without allowing Meta to access that data.
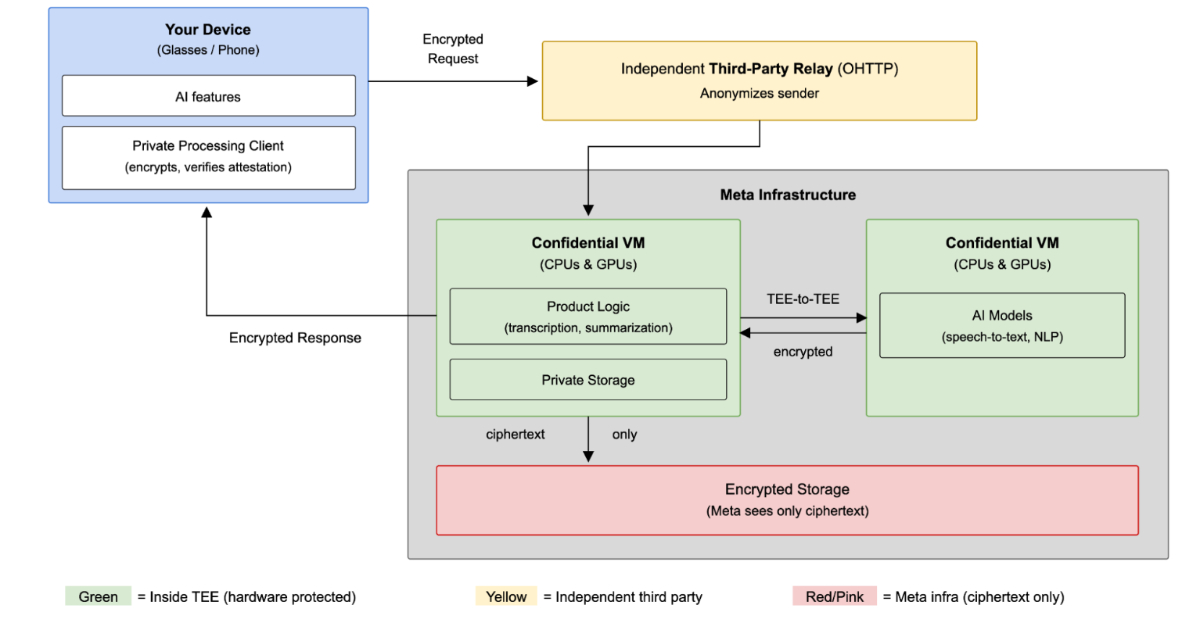
The architecture moves the confidential computing boundary from the device into Meta's cloud infrastructure. AI models run inside confidential virtual machines (CVMs) backed by hardware TEEs, with processor encrypted memory. Meta says the boundary spans CPUs and GPUs, allowing mixed workloads to remain protected.
Before transmitting personal context, the glasses perform remote attestation and establish an attested TLS session with a TEE. The device verifies a hardware-signed certificate and compares the workload measurement against an append-only transparency ledger. Failed verification prevents data transmission. Anonymous credentials and third-party OHTTP relays operated by Fastly or Cloudflare further separate user identity from request processing.

Meta's Private Processing architecture (Source: Meta Blog Post)
Persistent state remains inside the confidential boundary. Meta places the storage engine inside the TEE and encrypts data with user provided keys before it leaves the protected environment. Queries execute within the same boundary, limiting exposure of database access patterns.
Private Processing is built around hardware isolation, fail closed guarantees, public verifiability, non targetability, and encrypted storage. Production CVM images are registered in the transparency ledger. Because engineers cannot inspect protected memory or capture model inputs and outputs, Meta relies on aggregate operational signals such as CPU utilization, memory allocation, network latency, and hardware failure rates.
The privacy implications of always on wearable AI have also generated community discussion. In a Reddit discussion about Meta's glasses, one commenter argued that an assistant providing contextual information would need to continuously listen and observe its surroundings, highlighting the privacy implications of persistent sensing.
Deployment remains a limitation. WIRED reported that Private Processing is not yet available on Meta's glasses, and Meta has not specified which features will initially use the system or provided a timeline for its availability. Meta engineering director Pritam Shah said the platform is ready and working, but that Meta was announcing it before broader deployment to engage security and privacy researchers and a third party auditor.
Meta says it is working with independent security firms, including NCC Group, and security researchers to review the architecture and attestation mechanisms. The company also plans to provide researchers with CVM binaries, tools, and documentation as it expands the system for increasingly stateful, multimodal, and agentic AI experiences.
About the Author
Leela Kumili
Show moreShow less
— Originally published at infoq.com
Want this in your inbox every morning?
Daily brief at your local 8am — bilingual EN/中文, free.
More from InfoQ AI, ML & Data Engineering
See more →Google Cloud Workbench Notebooks Extension Connects VS Code to Google Cloud's Jupyter Notebooks
The Google Cloud Workbench Notebooks extension for VS Code allows developers to seamlessly connect their local IDE to managed Jupyter notebook environments on Google Cloud, enhancing ML workflow efficiency. This integration eliminates context switching, enabling smooth transitions from local experimentation to high-performance cloud computing.